Overview
horizon-issuer is an external issuer for cert-manager that allows to issue certificates through Horizon, EVERTRUST’s CLM. It relies on cert-manager, the industry standard for managing certificates in cloud-native environments to operate.
This usage of cert-manager brings multiple advantages:
-
Seamless integration into most workflows, since cert-manager is already the standard for requesting certificates;
-
Includes battle-tested features such as automatic certificate renewal, secret management, and more;
-
Benefit from cert-manager’s large ecosystem of integrations with other tools and platforms.
It interacts as a gateway between cert-manager and Horizon, handling CertificateRequests from cert-manager without having to access secrets such as private keys, which never leave the cluster:
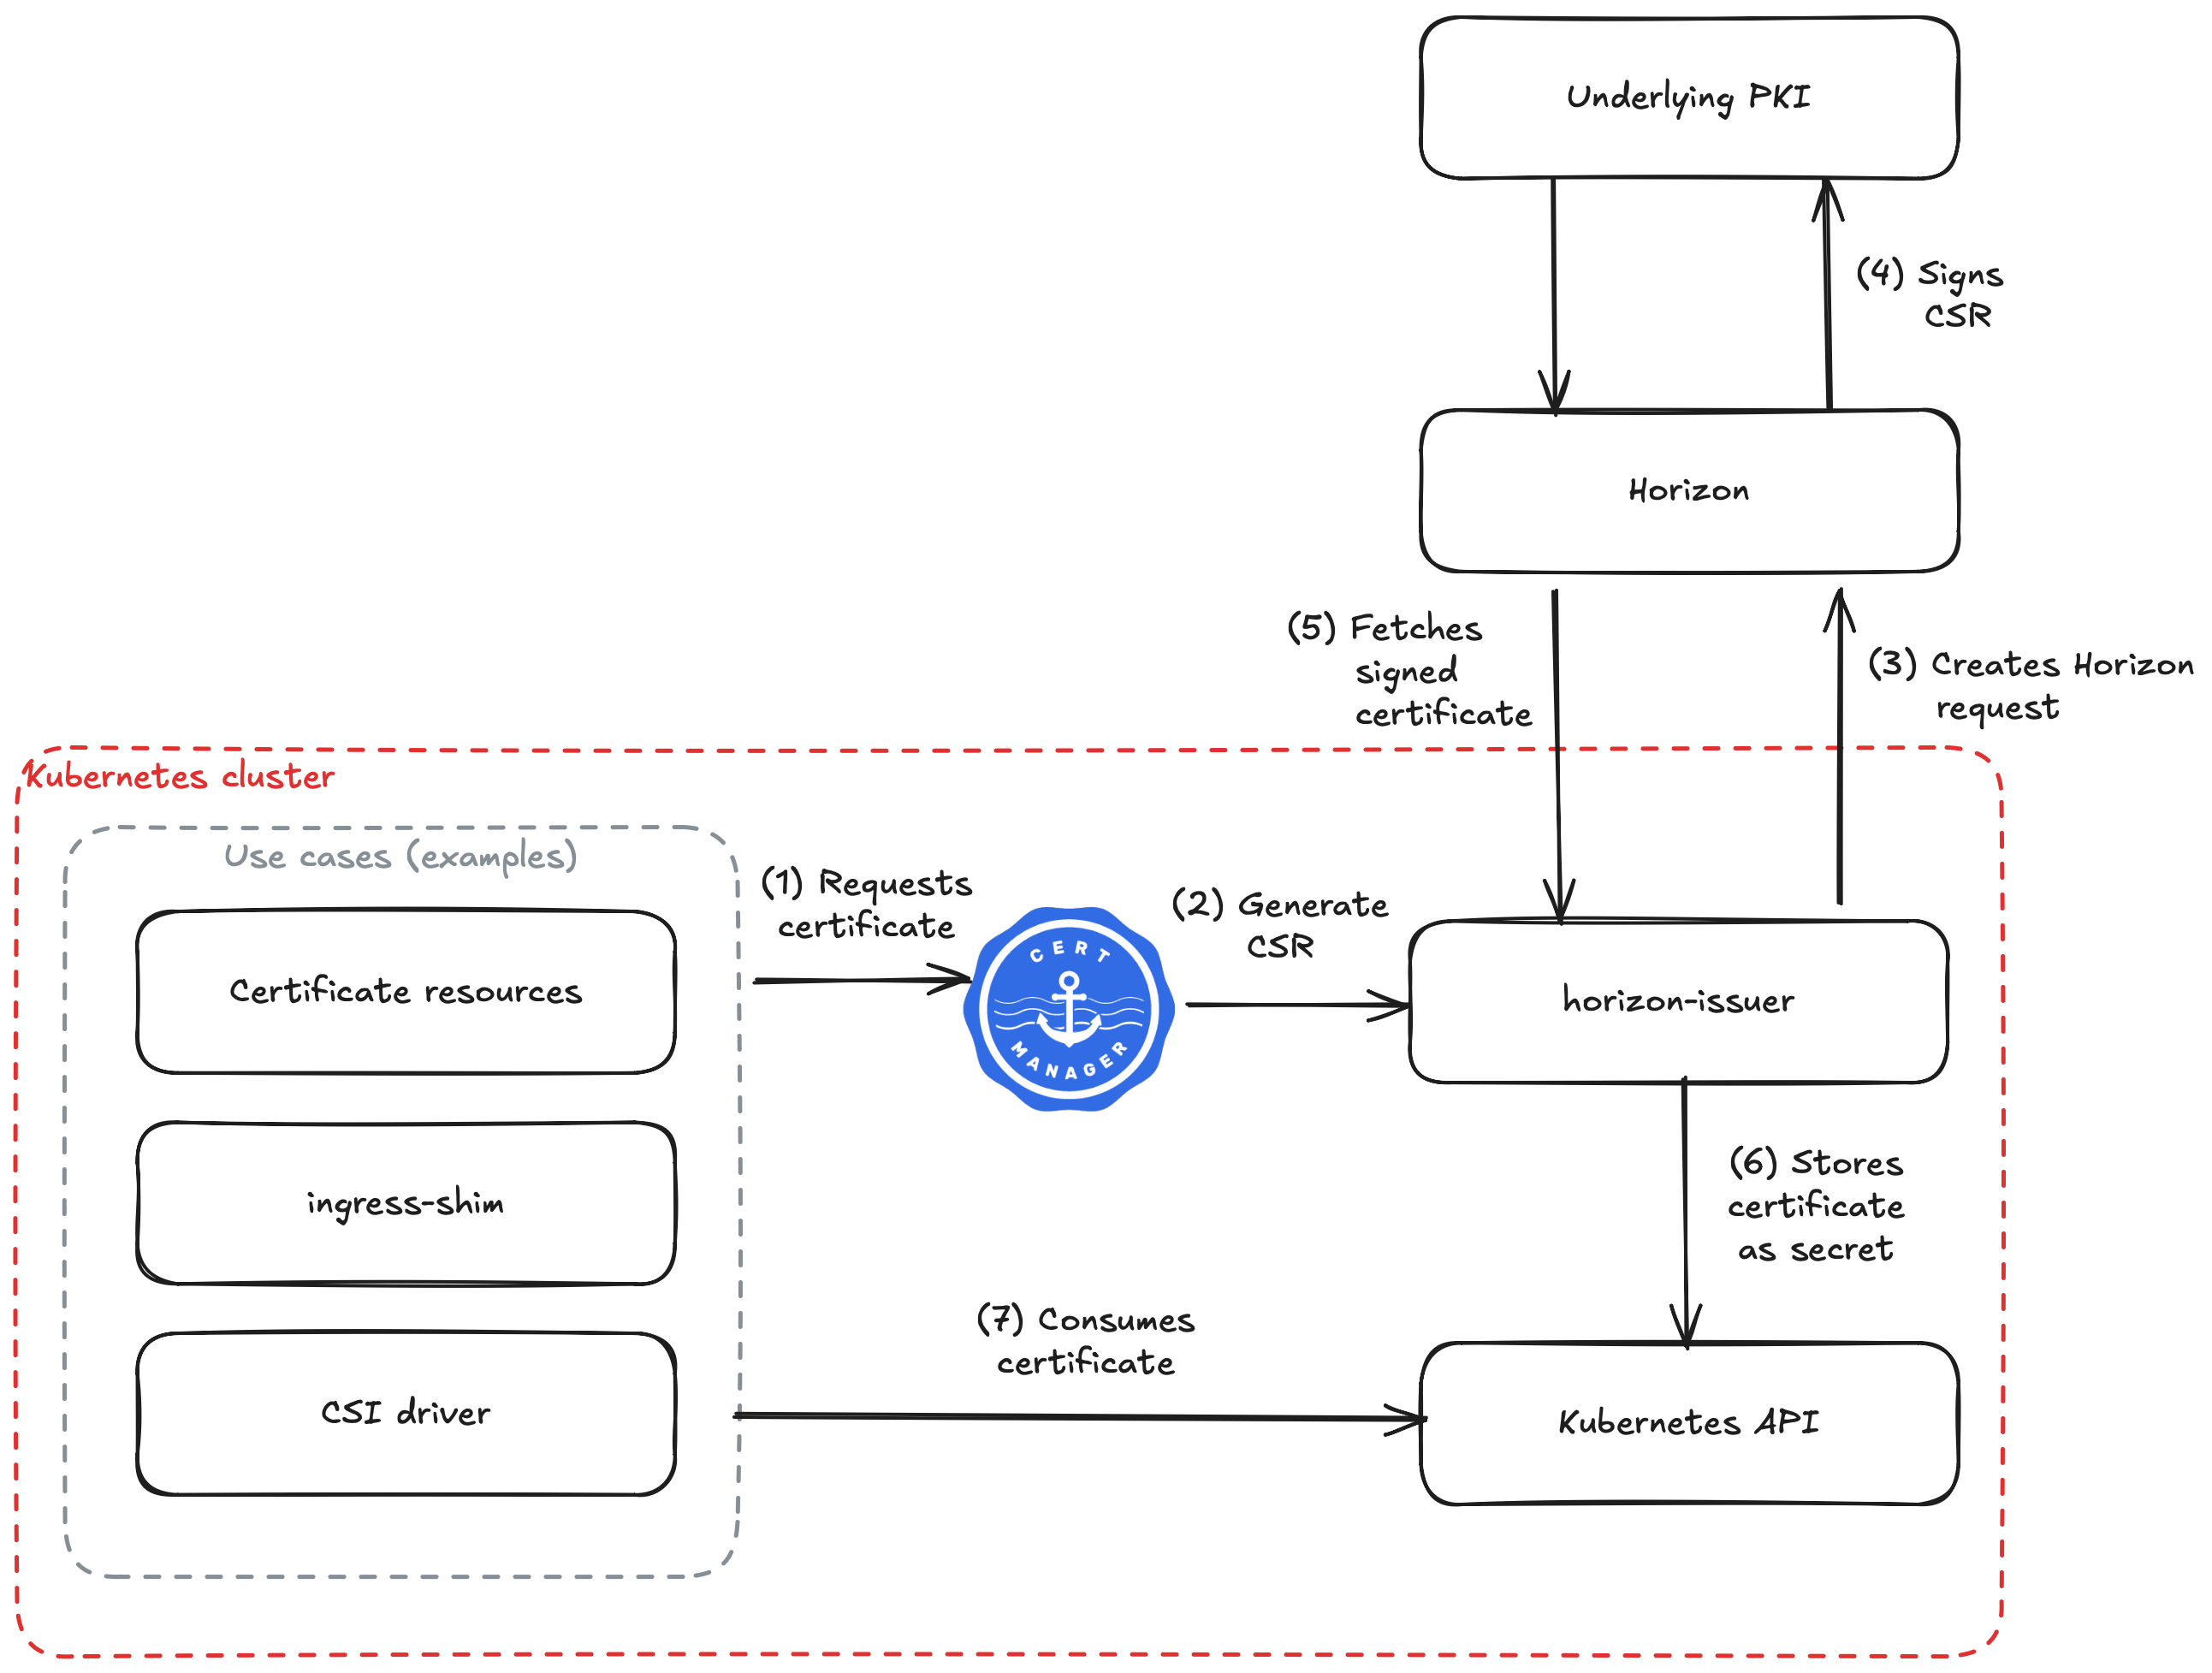
How a request moves through Horizon
horizon-issuer does not approve CertificateRequest objects. It submits them to Horizon whether or not something on the cluster has approved them, and it never sets the Approved or Denied conditions itself. If you want requests approved on the cluster, that is the job of the approval policies you run there, such as the cert-manager built-in approver or approver-policy. The only approval decision horizon-issuer reacts to is a denial, described below.
When cert-manager creates a CertificateRequest for a Horizon issuer, horizon-issuer submits an enrollment or renewal request to Horizon and stores two annotations on the CertificateRequest:
| Annotation | Content |
|---|---|
|
The identifier of the request on Horizon. Use it to find the request in the Horizon UI or API. |
|
The last status reported by Horizon: |
While the request is pending on Horizon, for instance because the issuer credentials only hold the "Request enroll" permission on the profile and an operator still has to approve it, the CertificateRequest keeps a Ready condition set to False with the Pending reason. horizon-issuer polls Horizon until the request finishes, then reports the outcome on the Ready condition:
-
a
completedrequest fillsstatus.certificateand setsReadytoTrue; -
a
deniedorcanceledrequest setsReadytoFalsewith theFailedreason and a failure time, so that cert-manager fails the parentCertificateand retries with backoff; -
a
failedrequest sets theInvalidRequestcondition with the error returned by Horizon.
Denial on the cluster
When an approver on the cluster sets the Denied condition on a CertificateRequest that horizon-issuer had already submitted, horizon-issuer cancels the request on Horizon if it is still pending there, so that nobody waits on it. It then sets Ready to False with the Denied reason and a failure time. If the cancellation fails, horizon-issuer retries it before closing the request.